Vai al contenuto principale

#southkorea

South Korean Church Breaches Expose More Than One Million Congregant Records

Read Time:3 Minute, 23 Second

Two major South Korean churches have suffered extensive intrusions that exposed records a

Altro...

Read Time:3 Minute, 23 Second

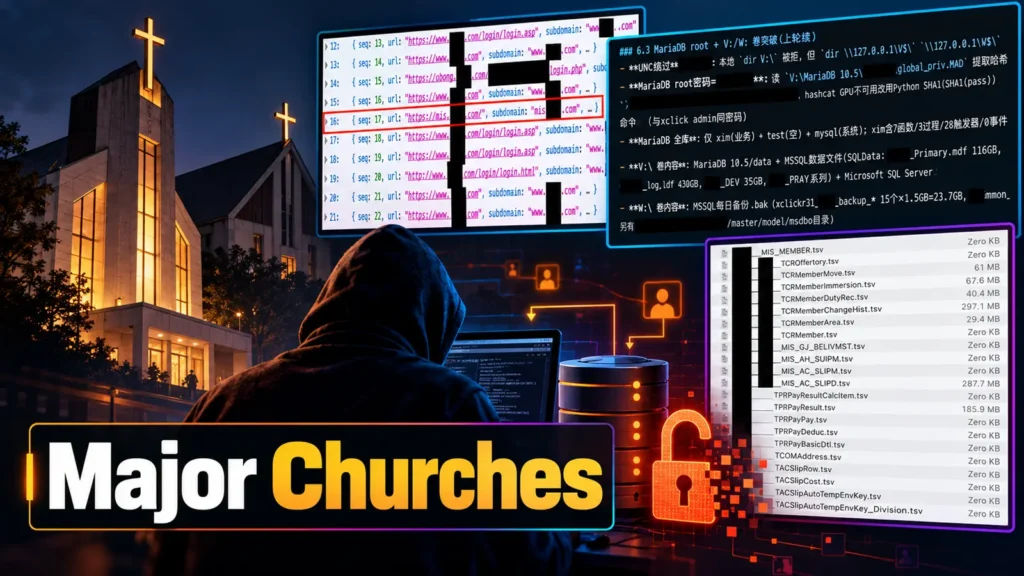
Two major South Korean churches have suffered extensive intrusions that exposed records associated with more than one million congregants, along with donation, payroll, employee and administrative information. The attacks followed different entry paths but converged on a common weakness: loosely controlled connections between public-facing applications, databases, internal services and cloud storage.

OASIS researchers reconstructed the activity from tools, stolen files and operator reports recovered from an attacker-controlled server. Their findings point to multi-stage intrusions involving application compromise, credential recovery, lateral movement and off-site staging rather than a single malware family. Because datasets can overlap, the precise number of unique people affected has not been independently confirmed.

A web shell opened the first environmentAt the first church, attackers gained a foothold through a web shell placed in an enterprise resource planning system. They reverse engineered ERP application components, decrypted database settings and obtained administrator access to Microsoft SQL Server. The attackers then used the database server’s xp_cmdshell capability to execute operating-system commands and move into linked systems.

From there, access expanded into membership, accounting, physical-access, library, chat and mail databases. The operators bypassed a database-monitoring control, recovered a MariaDB root password and found hardcoded network-attached storage credentials in backup-related configuration. The chain shows how one exposed application can become a bridge to several otherwise separate repositories.

The recovered collection contained approximately 960,000 congregant records updated during the previous two years, including names and South Korean resident registration numbers. It also included about 330,000 donation entries, 68,000 document-creation records, more than 14,000 chat messages and 6,874 login accounts. Investigators identified 47.3 GB across 13,939 files in a compromised MinIO bucket used for staging.

Leaked credentials and IDOR drove the second attackThe second church was reached through previously leaked credentials and authorization weaknesses in groupware and membership services. Insecure direct object reference flaws occur when an application accepts a record identifier supplied by a user but does not confirm that the user is permitted to view or change that record.

Using a valid member session, the attackers could access other users’ plaintext PINs and reset an account with manager-level privileges. They obtained roughly 89,000 congregant records, 383 employee records, 286 human-resources entries, 96 employee photographs and internal approval documents. Researchers also found exposed college-ministry APIs and cloud storage that allowed unrestricted reading and writing.

These details underline why valid credentials cannot substitute for authorization. Every request for a record must be checked against the current user’s privileges, even after authentication succeeds. Password-reset functions require especially strong safeguards because they can turn limited access into account takeover.

Connected systems multiplied the damageIn the first environment, the attack progressed from an internet-facing ERP component to database administration, operating-system execution, backup storage and cloud staging. In the second, a combination of exposed credentials and missing object-level checks crossed groupware, membership, SAP and storage services. Hardcoded secrets and excessive service privileges allowed the operators to keep moving after the initial compromise.

Religious and community organizations can hold a uniquely sensitive mix of identity, family, donation and communication data. Criminals could use that material for identity fraud, tailored phishing, extortion or scams that exploit trust within a congregation.

Containment and prevention stepsRemove unauthorized web shells and preserve forensic copies before rebuilding affected application servers.

Rotate database, NAS, cloud and application credentials; revoke tokens and invalidate active sessions.

Disable xp_cmdshell where it is not operationally necessary and constrain linked-server privileges.

Review ERP, SQL Server, NAS and cloud logs for unusual exports, bulk downloads and unexpected external connections.

Test every sensitive API for object-level authorization and strengthen privileged password-reset workflows.

Eliminate secrets from source code, configuration backups and publicly reachable storage.

Organizations should also alert affected people with clear guidance about targeted fraud and credential reuse. The broader lesson is architectural: segmentation, least privilege and enforced authorization can stop an initial application breach from becoming an organization-wide data loss event.
#databreach #southkorea #idor #webshell

0

Caricamento...

0
0

Caricamento...

South Korea Orders Financial-Sector Security Review After Wave of Data Breaches

Read Time:4 Minute, 1 Second

South Korea has ordered a sweeping investigation into a series of breaches across its fina

Altro...

Read Time:4 Minute, 1 Second

South Korea has ordered a sweeping investigation into a series of breaches across its financial sector after banks, lenders and finance companies disclosed the exposure of sensitive personal information. President Lee Jae Myung directed officials to examine the incidents in full and develop stronger safeguards, elevating what had appeared to be separate company-level events into a national cybersecurity priority.

The response follows disclosures from several institutions in the opening days of October. Although the reported victim counts and affected systems vary widely, the incidents share an uncomfortable theme: business-support platforms outside the core banking environment can still contain valuable identity and credit data. Authorities are now investigating whether the attacks are related and whether automation or artificial intelligence assisted the intruders.

Multiple Institutions Report Exposed Personal DataShinhan Bank reported the largest breach among the major banks, affecting roughly 25,000 customers. The exposed records included names, telephone numbers, annual income and loan limits. Some files also contained resident registration numbers, making the incident more serious because those identifiers can support identity fraud and highly convincing social-engineering attacks.

KB Kookmin Bank and Hana Bank announced smaller but still sensitive exposures. KB said information belonging to 119 customers leaked through a mobile work-support system used by employees. Hana identified abnormal access to an operations-support system involving 89 customers. The affected Hana records reportedly included names, national identification numbers, addresses, email addresses, phone numbers and employer details.

Other organizations also reported incidents. Yegaram Savings Bank said approximately 40,000 customers were affected, while Hyundai Capital disclosed exposure involving 146 housing-loan agents. BNK Busan Bank separately reported information linked to 11 outsourced workers. These numbers refer to different populations and should not be combined into a single confirmed victim total.

AI Clues Do Not Yet Prove a Unified CampaignLocal reporting cited traces of an AI-based automation tool in the Shinhan investigation, while another report said several attacks used common IP addresses. Those clues may help investigators connect infrastructure or methods, but they do not yet establish that one threat actor conducted every intrusion. Nor do they show that an autonomous AI system independently carried out the compromises.

No complete public attack chain has been released. Authorities have not identified a common vulnerability, named malware family or definitive set of indicators spanning all affected institutions. The known access points also appear to include loan-agent websites and internal employee-support tools rather than only public online-banking applications. That distinction matters for both attribution and remediation.

Support Systems Create a Wider Attack SurfaceKB and Hana reportedly said the affected environments were separated from their internet and mobile banking services, and that the incidents did not expose customer transaction data. Segmentation may have limited the immediate financial impact, but it did not prevent the loss of information that criminals can use for follow-on fraud.

The pattern is a reminder that security programs must cover the entire financial-services ecosystem, including:

employee portals and mobile work-support applications;

loan-agent, contractor and outsourced-service platforms;

operations systems holding identity and credit information;

third-party connections with access to customer records; and

logs capable of linking unusual access across separate environments.

Systems considered secondary to the main banking platform can receive less monitoring and slower security investment, even when they store highly sensitive records. Attackers can exploit that imbalance, targeting a weaker application to obtain data suitable for impersonation, phishing or loan fraud without ever entering the core transaction network.

What Authorities and Financial Firms Need to EstablishPolice began examining the incidents on October 2, and financial authorities ordered broader checks at banks and card companies. The most urgent questions are whether the same infrastructure appears in multiple breaches, how attackers first gained access, whether compromised third parties created shared exposure, and what role automation played after entry.

Affected firms should preserve authentication, web, endpoint and administrative logs before retention windows erase useful evidence. They should also review privileged access to support systems, rotate potentially exposed credentials, validate network separation and notify people whose identification data may be misused. Monitoring should extend beyond direct account theft to targeted phishing and fraudulent credit applications.

For customers, the disclosures warrant extra caution around messages that reference real loan details, employers or contact information. Accurate personal data can make a fraudulent call or email appear legitimate. Requests to disclose passwords, one-time codes or transfer funds should be verified through an institution’s official channel rather than through contact details supplied in the message.

The investigation may eventually show several unrelated breaches rather than one coordinated operation. Even so, South Korea’s sector-wide response reflects the broader lesson: financial security depends on every system that collects, processes or supports sensitive customer information, not only the applications that move money.

Source: Cyber Security News.

#databreach #artificialintelligence #southkorea #financialsector

0

Caricamento...

0
0

Caricamento...